SUPPLY CHAIN ECOSYSTEM SECURITY

Secure Your Supply Chain. Strengthen Your Business.​

PexLens helps organizations identify, assess, and manage risks across their supply-chain ecosystem.​

How PexLens Works

SCAN

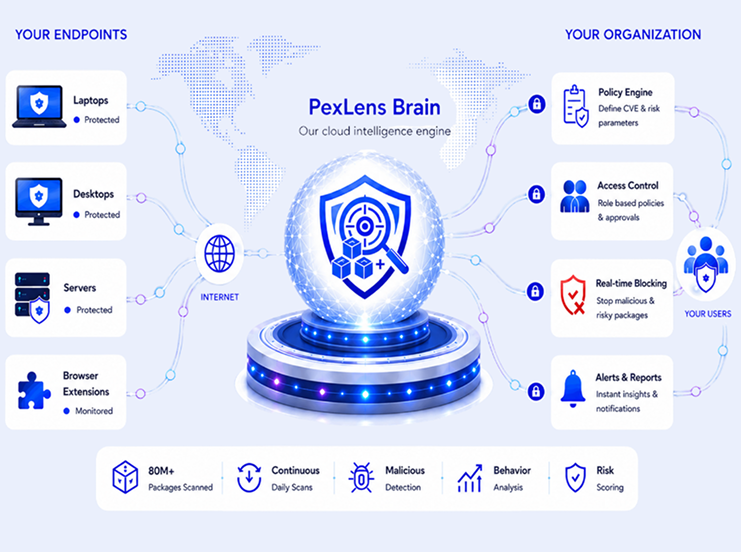
Scan endpoints for packages & browser extensions
COLLECT

Send inventory to PexLens Brain securely

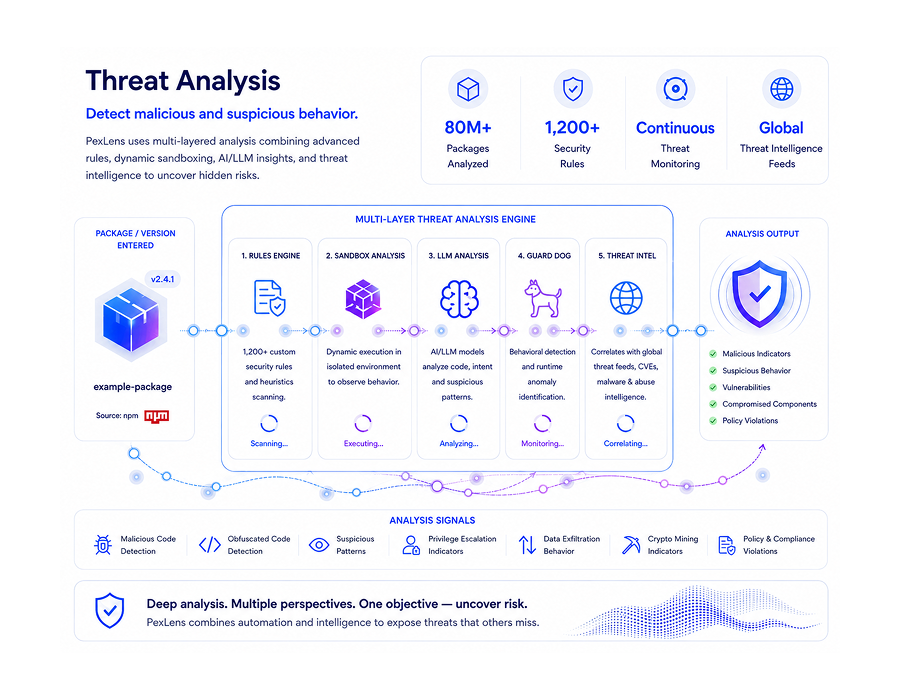
ANALYZE

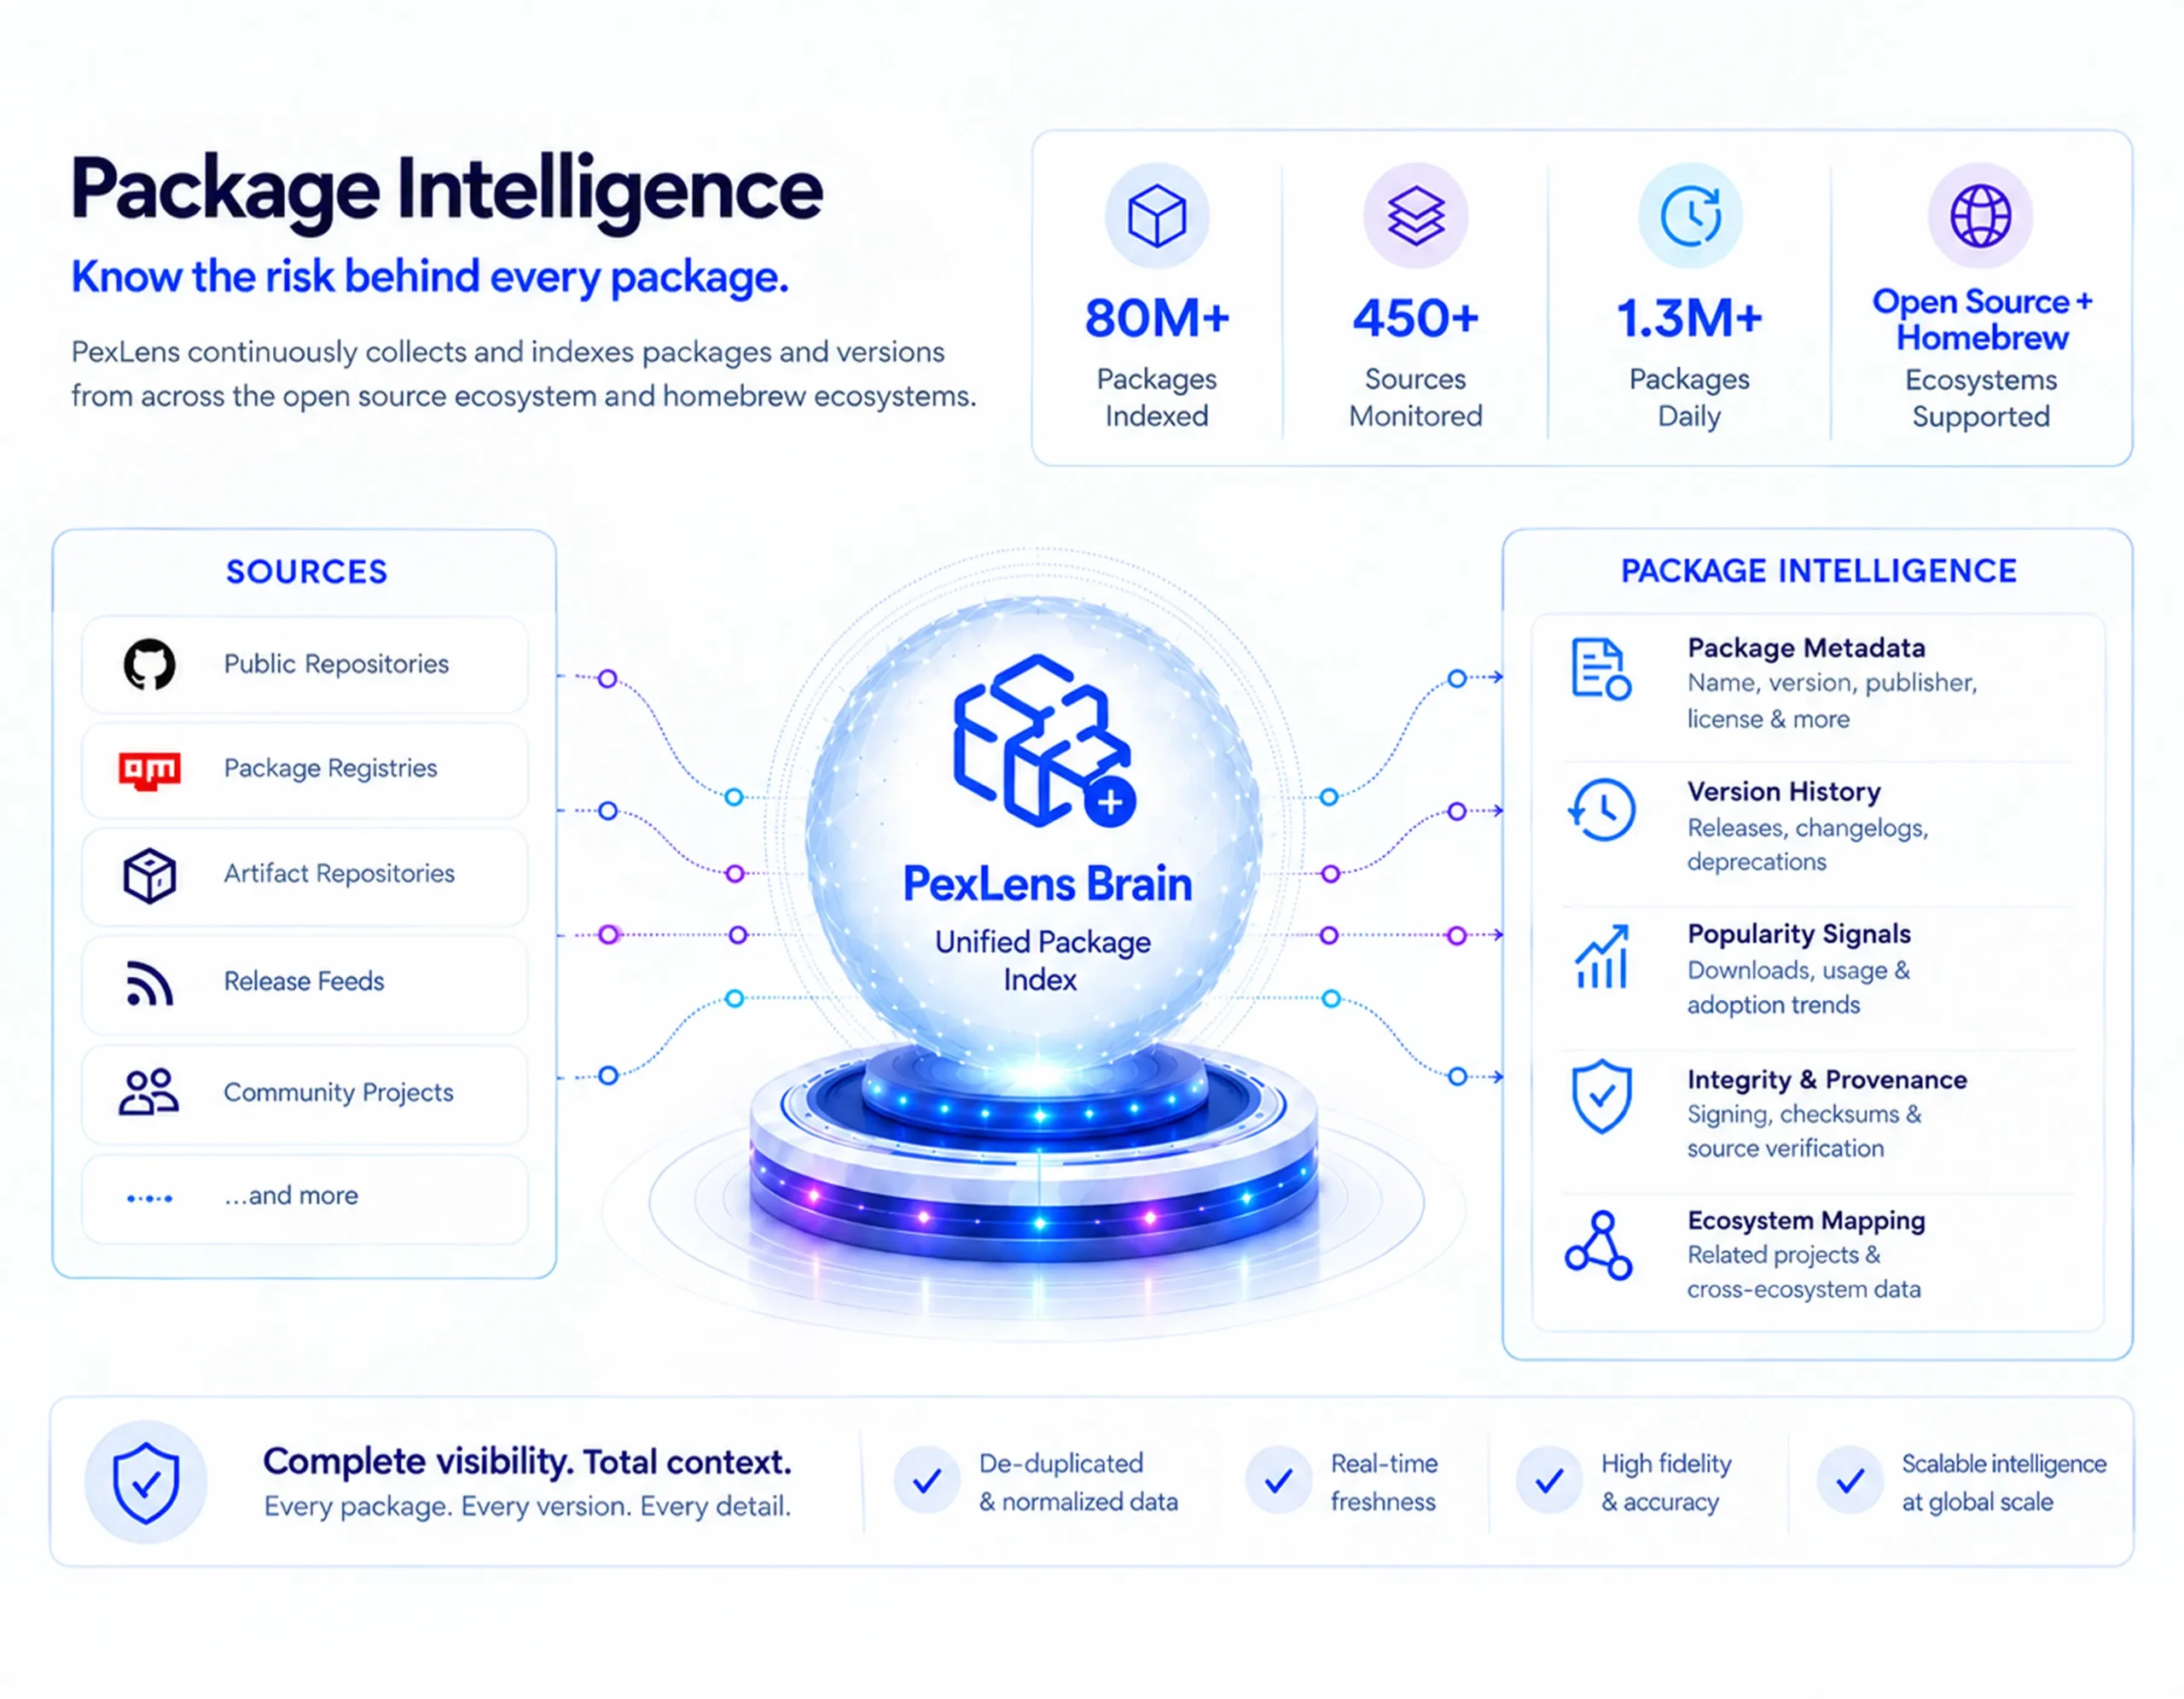
Analyze against 80M+ packages & behavior patterns

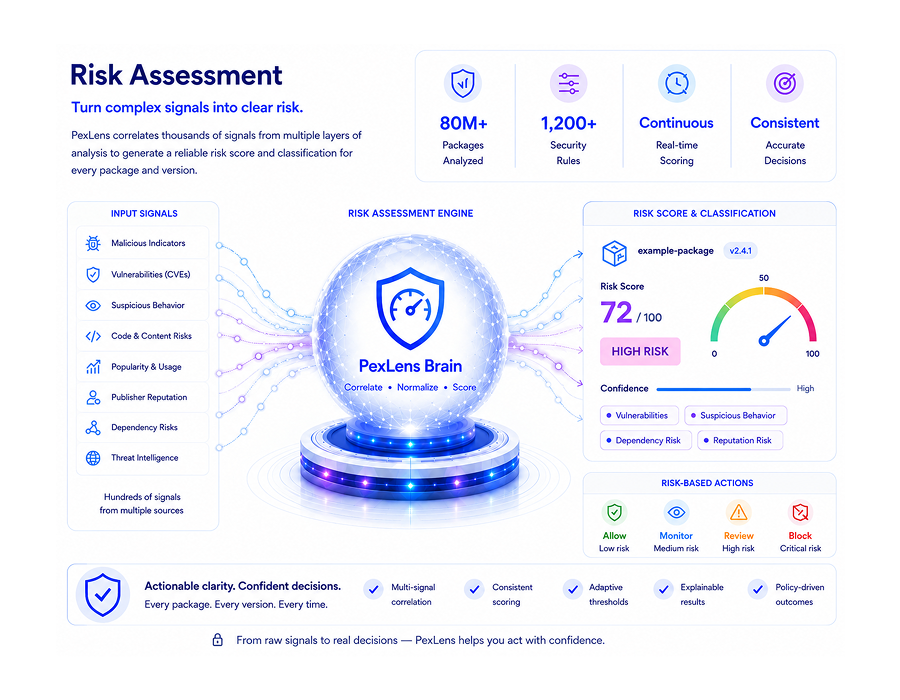
SCORE

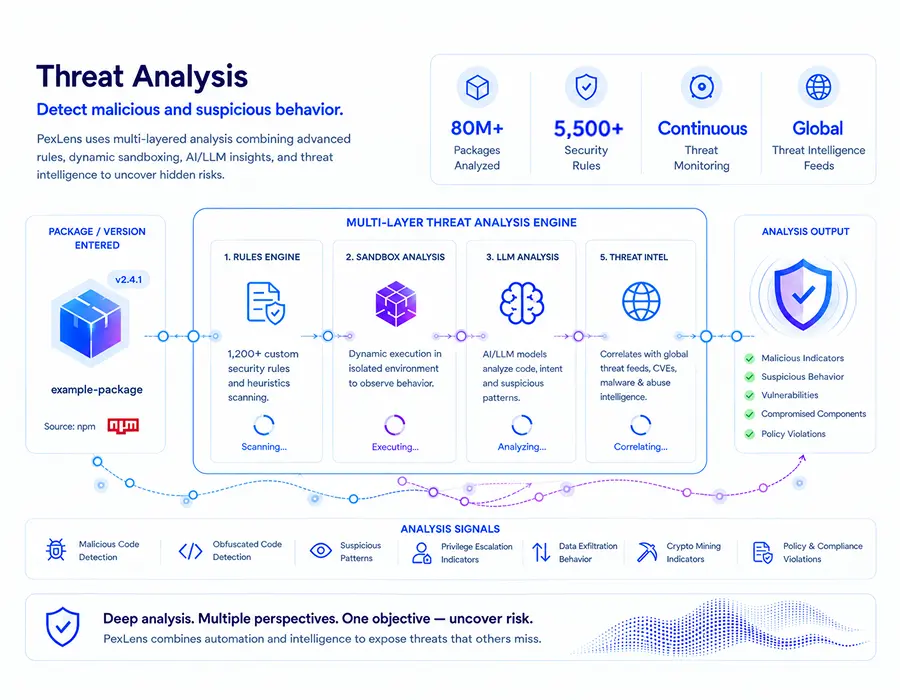
Score for risk, malware, suspicious behavior & reliability

PROTECT

Block threats. Enforce policies. Keep your organization safe

Software Supply Chain Security
Real-time Protection
Malware & Risk Detection
Policy-driven Control
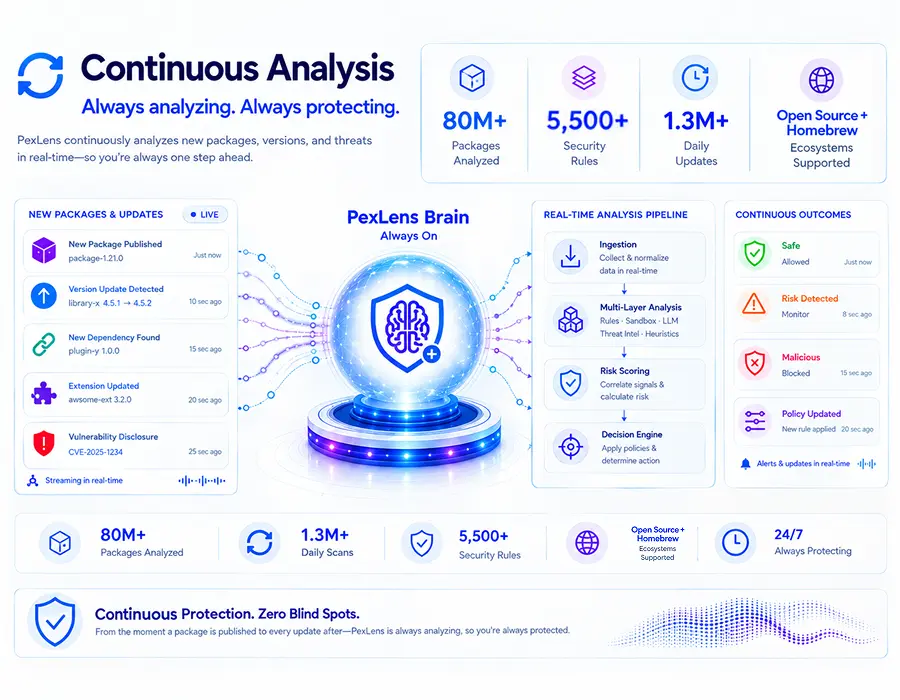
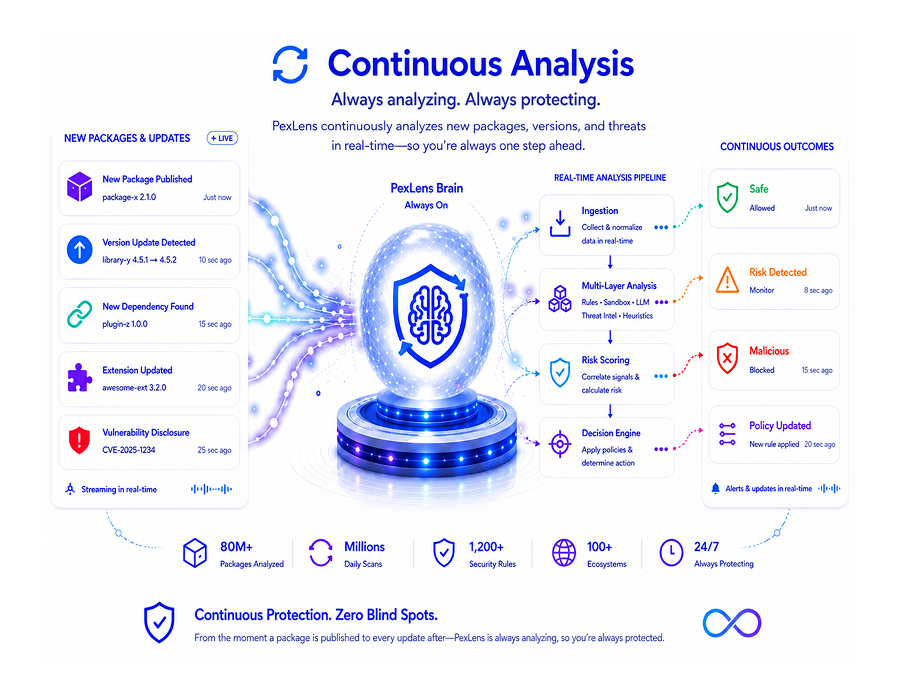
Continuous Intelligence
Enterprise Ready

THE SOFTWARE SUPPLY CHAIN

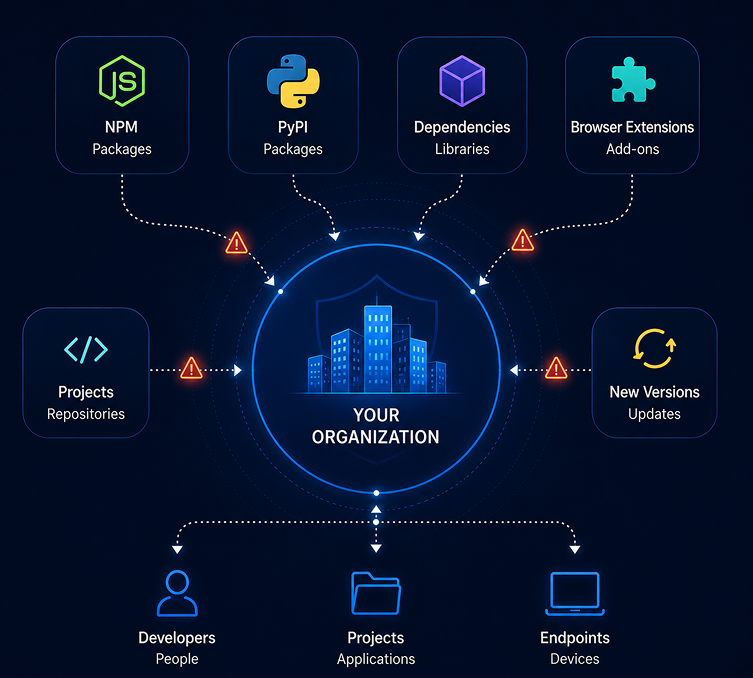
Every package, dependency and browser extension can become an entry point.

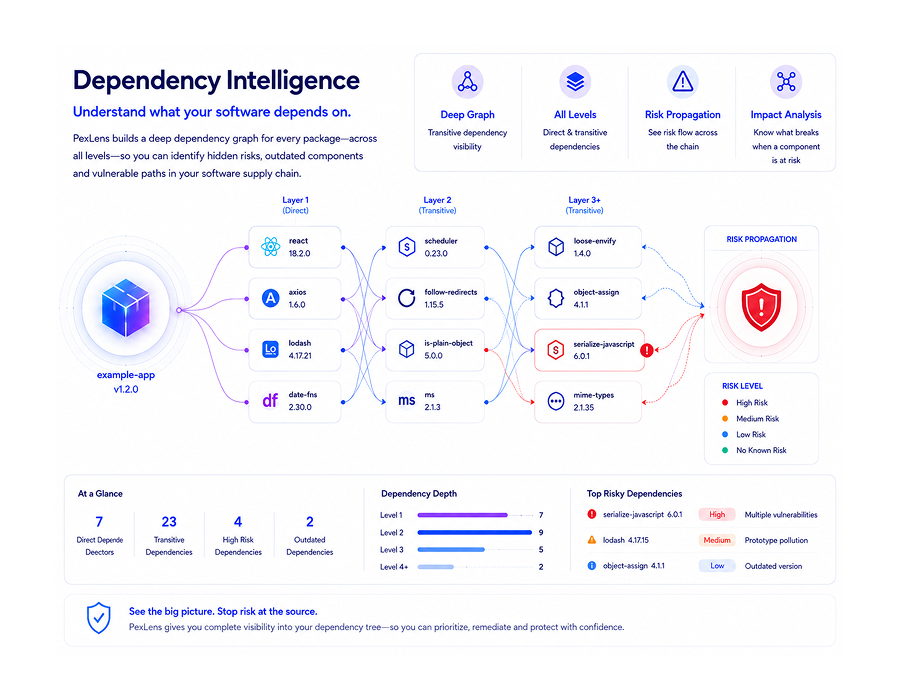
Modern organizations rely on thousands of software components that change every day. Without visibility and control, a single compromised or vulnerable component can introduce risk into the organization.

Your software ecosystem is constantly changing.
Do you know what you're allowing in?

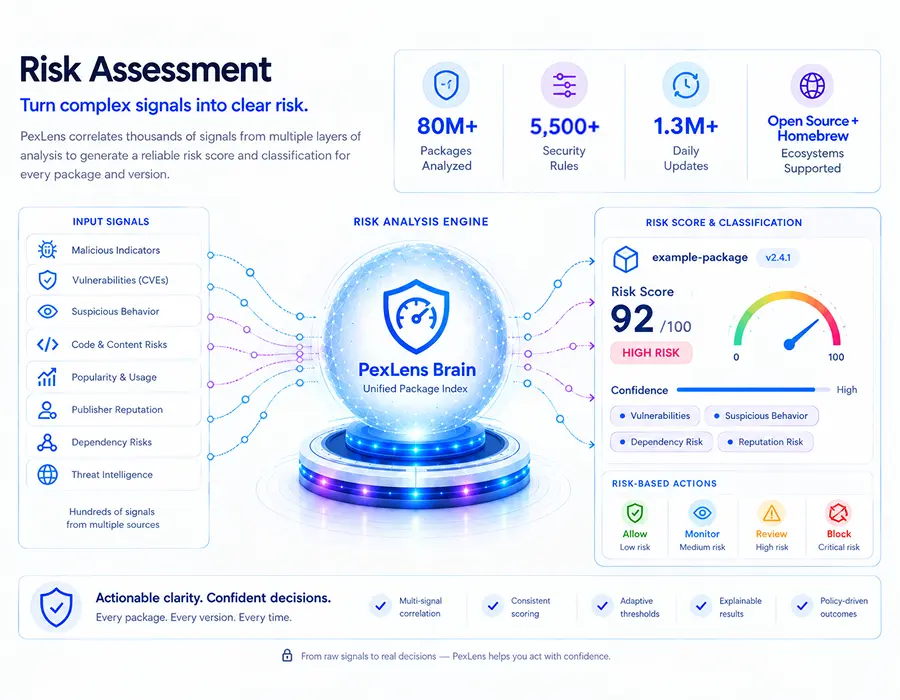
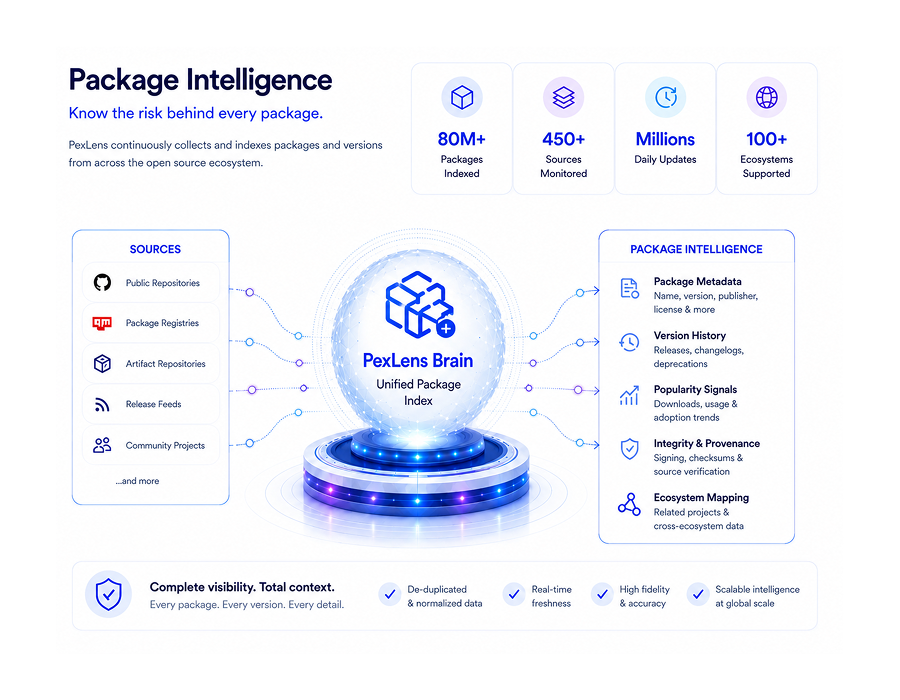
THE PEXLENS BRAIN

Intelligence behind every package and extension 

REAL-TIME PROTECTION

Stop threats before they reach your endpoints​
PexLens evaluates package requests in real time and applies your organization's security policies ​ before software is installed​

The decision engine

Policy-driven decisions​
Apply your own security thresholds to every package request​

From detection to action

Protection doesn't stop at detection​
When PexLens identifies a threat, your organization can ​respond immediately -with automated blocking, real-time notifications​and administrator-led remediation​

What PexLens Protects Against​

Protect Against the Risks Hidden in Your Software Supply Chain​

Malicious Packages

Stop packages containing malicious code.

Vulnerable Components

Enforce your organization’s CVE thresholds.

Compromised Dependencies

Identify compromised or suspicious components.

Supply-Chain Attacks

Detect threats before they reach endpoints.

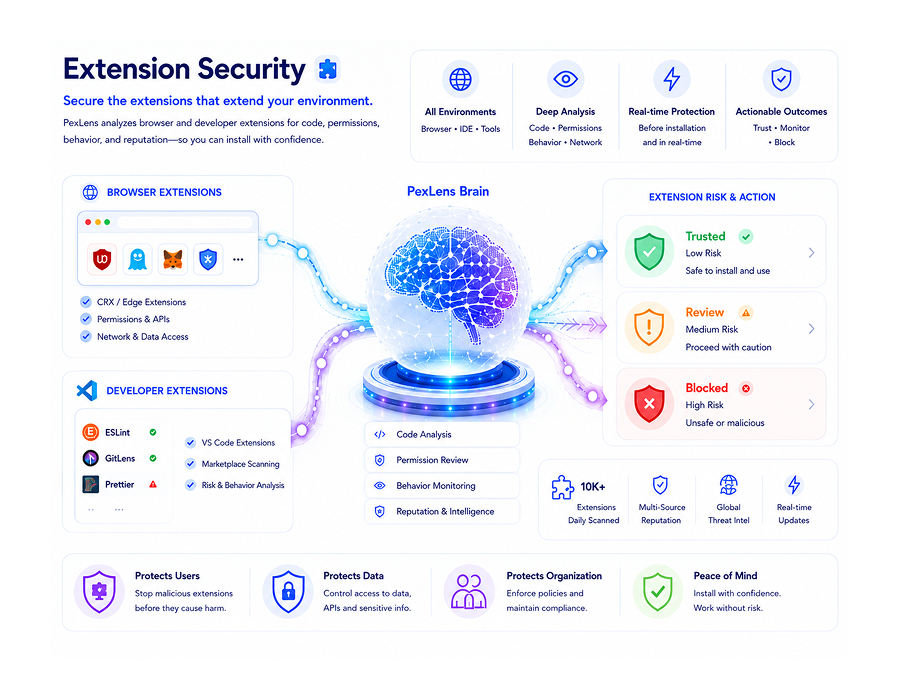
Malicious Extensions

Assess browser and developer extensions.

Policy Violations

Prevent software that violates organizational security policies.

See Your Software Supply Chain Clearly

Discover packages, dependencies, extensions, threats and affected endpoints from one place.​

Built for the Teams Responsible for Security

Security Leadership

Understand your software supply-chain exposure and enforce organizational risk policies.

Application Security / DevSecOps

Assess packages, dependencies and extensions before they introduce risk.

IT & Endpoint Security

Discover software across endpoints and respond to threats quickly.

From Detection to Action​

Know What Enters Your Organization. Control What Stays​
PexLens brings software supply-chain intelligence, real-time protection ​ and policy enforcement into one platform​

FAQ

Collapsable panel with such questions​